Australian authorities have arrested and charged two men, aged 21 and 23, who. Police say belong to TeamPCP, a hacking. Group behind a wave of software supply-chain attacks. These attacks hit over 1,000 organizations worldwide. And they led to the theft of about 500,000 credentials and 300GB of data. This guide covers the Australia arrests of the alleged TeamPCP hackers behind supply-chain attacks in detail. This guide covers the Australia arrests of the alleged TeamPCP hackers behind supply-chain attacks in detail. This guide covers the Australia arrests of the alleged TeamPCP hackers behind supply-chain attacks in detail.
Australia arrests alleged TeamPCP hackers behind supply-chain attacks: What Is TeamPCP and How Did They Operate?
TeamPCP is not a traditional group with a clear chain of command. And instead it is a loose group of threat actors who work together through hacking forums, Discord servers. And Telegram channels. According to the Australian Federal Police (AFP), the group injected malicious code into. Open-source software packages hosted on public repositories. And developers did not know these packages were harmful. So they added them to apps used by government agencies, schools. And private companies around the world. High-profile victims include Trivy, LiteLLM, Telnyx, SAP, TanStack, the European Commission, Mistral AI, OpenAI, and GitHub.

How Were the Suspects Identified and Arrested?
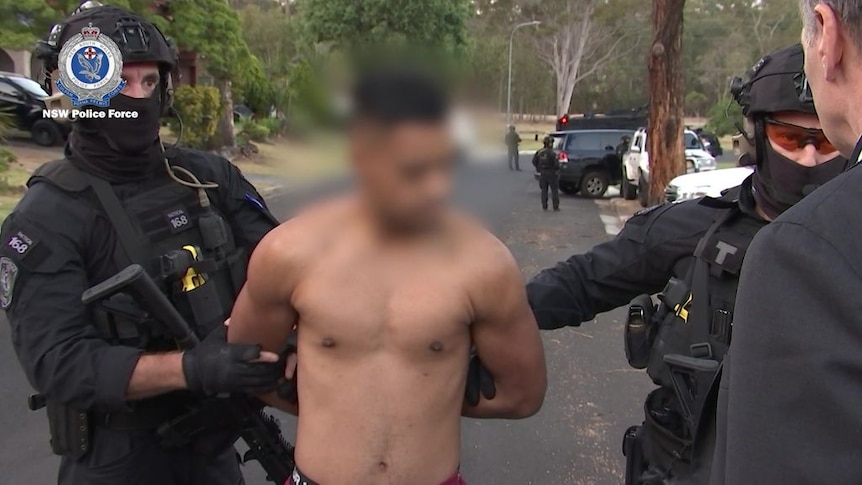
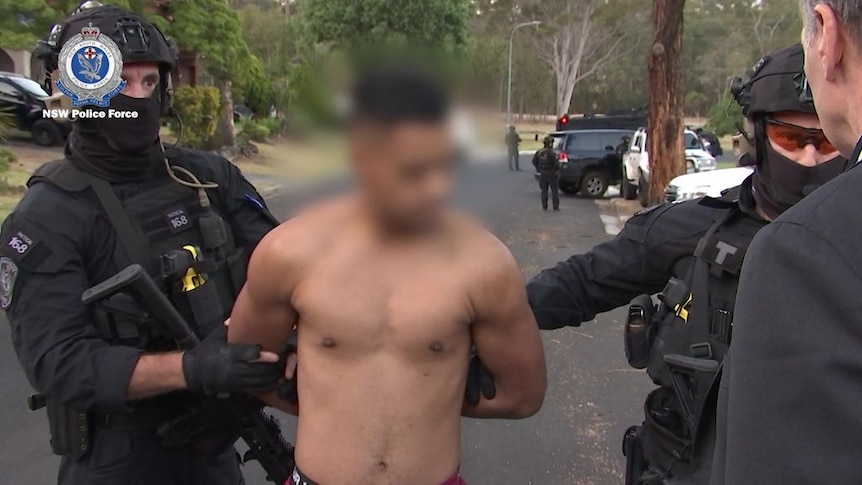
The investigation started in April 2026 after the AFP and FBI got tips from security firms. On August 26, 2026, officers arrested the two men in Cottesloe and Mandurah, Western Australia. And police also seized electronic devices for forensic analysis. Police say the suspects got cryptocurrency payments for their role in TeamPCP operations. And after the arrests, the security firm Flare and journalist Brian Krebs ran. Their own investigations, linking alleged TeamPCP members to real names through reused aliases, Telegram activity. And other online traces.
What Charges Do the Suspects Face?
The two men face a combined 14 charges. Which include possessing and supplying data for computer offenses. And modifying data to help carry out serious crimes. The younger suspect also faces charges for allegedly dealing with at least $100,000 in criminal proceeds. And he also faces a charge for failing to comply with an order. To give access to electronic data. Maximum penalties range from 3 to 20 years in prison per charge. And the AFP has not ruled out more arrests as forensic analysis of seized evidence continues.
Why This Matters for Software Supply-Chain Security
The TeamPCP case shows the broad risk. That comes from injecting malicious code into trusted open-source dependencies. Because a single compromised package can spread across thousands of downstream apps, giving attackers valid credentials. That get past normal perimeter defenses. The AFP puts global cleanup costs in the hundreds of millions of dollars. And this incident highlights the need for software bill of materials (SBOM) adoption, dependency scanning. And runtime checks of open-source components in production environments.
What's Next for the Investigation and Industry Response
Forensic analysis of seized devices may uncover more collaborators, infrastructure, and victim data. And the AFP and FBI continue to work with international partners. For developers and security teams, the case is a reminder to enforce signed. Commits, watch for dependency changes. And put in place credential rotation policies. Expect more regulatory scrutiny on software supply-chain openness after this and similar incidents.
Key Points
Two men arrested in Western Australia on August 26, 2026. And charged with 14 offenses linked to TeamPCP supply-chain attacks.
Attacks compromised over 1,000 organizations, stole 500,000 credentials and 300GB of data, with. Cleanup costs in the hundreds of millions.
TeamPCP worked as a loose group via forums, Discord. And Telegram, injecting malicious code into open-source packages.
Investigation began April 2026 after tips from security firms. And Flare and Brian Krebs later linked aliases to real identities.
AFP has not ruled out more arrests as forensic analysis of seized devices continues.
The Bottom Line
The TeamPCP arrests show that law enforcement can break into decentralized cybercrime networks. But the scale of the compromise shows how open the software supply chain. Still is to credential theft through poisoned open-source dependencies.
Related Resources
For more context, check our related guides.